YAPRA Logo
yapra.ai

LOGIC BY DESIGN.

FLOW BY AI.

The open, transparent, and strictly governed deterministic core. Built on mathematical proof, hard boundary rules, and cryptographic state receipts.

YAPRA GOVERNED AGENTS
YAPRA Pure Glass EmblemYAPRA Amber Neural Branches Emblem

DETERMINISTIC PLATFORM CORE

Hard Boundary Rules Cryptographic SHA-256 Receipts Zero Hallucination-Induced Mutation
Scroll to ignite flow
Platform Foundations

AI Agents You Can Actually Trust With Your Business.

YAPRA is not a probabilistic chatbot that guesses under pressure. It is a sovereign, self-contained AI agent runtime engineered for zero unsigned mutation—ensuring zero state changes commit without an authorized cryptographic signature—with complete data isolation and hard deterministic verification at every step.

GLOBAL FINANCIAL RECONCILIATION

“Match $45,000 supplier invoice against ERP procurement records, verify department delegation ceilings, and execute authorized settlement.”

Latency SLA
0.28 ms
Decision & Check Latency
Factual Truth
100% Factual
Zero Hallucination
Policy Boundary
Ceiling Enforced
Budget Protected
State Mutation
ERP PO Committed
Cryptographically Sealed
Target Production SLA <0.4ms deterministic pre-action gate check
YAPRA Operational Substrate
3 CONCENTRIC EXECUTION RINGS
YAPRA 3D HDR Concentric Glass Ripples & Neural Crystal Leaf
01 // CORE OPERATIONS
Deterministic Core & Invariant Gates
DETAILS
02 // PRODUCTION-GRADE MODEL
Live Organizational Entity Twin (SARC)
DETAILS
03 // NATIVE COUPLING
Direct SCADA & ERP Integration
DETAILS
01RUNTIME INTEGRITY

Hard Deterministic Guardrails

AI never acts alone or unbounded; budget ceilings, role hierarchies, and transaction thresholds are mathematically unbreachable.

Tap to collapse specifications ↑
ACTIVE RUNTIME
POLICY GATES: STRICT ENFORCEMENT
Hard Deterministic Guardrails

Conventional LLMs extrapolate and guess when uncertain, creating severe operational risk. YAPRA enforces immutable, deterministic policy gates between neural reasoning and system execution. Unverified claims never execute; unauthorized API mutations are deterministically blocked before network dispatch.

Unsigned Mutation Risk
0.00% at Egress
Policy Verification
Runtime Gate Check
Unverified Execution
Instantly Blocked

Hard, immutable boundary rules are set in versioned code—not soft LLM prompts. Zero unsigned mutation.

02TOTAL SOVEREIGNTY

Sovereign & Air-Gapped Deployment

Your data never crosses organizational perimeters. Operates inside your private VPC or completely air-gapped on-premises data centers.

Tap to view details & 3D model ↓
03NO MODEL DRIFT

Governed Self-Learning & Live Model

Agents plan on an active model of equipment, ERP inventory, and shift rosters—learning from edge cases safely through automated regression checks.

Tap to view details & 3D model ↓
04DEEP INTEGRATION

Deep Runtime System Coupling

Not a cosmetic side-panel chatbot; hard-wired directly into SCADA sensor streams, live ERP stock, and shift rosters.

Tap to view details & 3D model ↓

01. Hard Deterministic Guardrails — Deterministic Policy Enforcement Gates

AI never acts alone or unbounded; budget ceilings, role hierarchies, and transaction thresholds are mathematically unbreachable.

Conventional LLMs extrapolate and guess when uncertain, creating severe operational risk. YAPRA enforces immutable, deterministic policy gates between neural reasoning and system execution. Unverified claims never execute; unauthorized API mutations are deterministically blocked before network dispatch.

Architectural Rule: Hard, immutable boundary rules are set in versioned code—not soft LLM prompts. Zero unsigned mutation.

  • Unsigned Mutation Risk: 0.00% at Egress
  • Policy Verification: Runtime Gate Check
  • Unverified Execution: Instantly Blocked

02. Sovereign & Air-Gapped Deployment — Zero Public Internet Leaks · Dedicated VPC or On-Prem

Your data never crosses organizational perimeters. Operates inside your private VPC or completely air-gapped on-premises data centers.

Engineered for mission-critical operations and highly sensitive enterprise data. Not a single byte of telemetry or operational data leaks to external APIs or multi-tenant clouds. The entire agent runtime, data platform, and models live strictly within your isolated physical or private cloud perimeter.

Architectural Rule: Absolute deployment sovereignty. Your models, weights, data, and execution traces never leave your perimeter.

  • External Uplink: Completely Disconnected
  • Telemetry Egress: Zero (Local Logs Only)
  • Infrastructure: Dedicated Single-Tenant

03. Governed Self-Learning & Live Model — Live Operational Entity Graph · Regression Gauntlet · Provable Exit

Agents plan on an active model of equipment, ERP inventory, and shift rosters—learning from edge cases safely through automated regression checks.

YAPRA represents your physical assets, live ERP inventory, and technician rosters in an active operational graph. When operators accept or modify recommendations, resolutions index into episodic memory—validated through automated regression gauntlets before promotion. Your operational knowledge stays 100% portable with Provable Exit.

Architectural Rule: Continuous improvement without operational instability. An enterprise asset that compounds in value safely.

  • Operational Graph: Live Assets & ERP Stock
  • Learning Updates: Regression Gauntlet
  • Data Portability: 100% Provable Exit

04. Deep Runtime System Coupling — Dynamic Impact Propagation · SCADA & ERP Integration · Zero Downtime

Not a cosmetic side-panel chatbot; hard-wired directly into SCADA sensor streams, live ERP stock, and shift rosters.

When an operational variable shifts—a sensor flags thermal drift or a spare part is delayed—YAPRA traverses dependency edges in real-time, re-evaluating only affected work orders. It executes routine updates with sub-millisecond latency (<0.4ms), but automatically halts and escalates to human approval on critical thresholds.

Architectural Rule: A true labor multiplier running directly inside application stacks and message brokers, rather than a side-panel bot.

  • Connected Systems: SCADA / ERP / CRM / APIs
  • Impact Resolution: Dynamic Topological
  • Halt & Escalate: Policy Verified
Tripartite Execution Topology

Platform Architecture

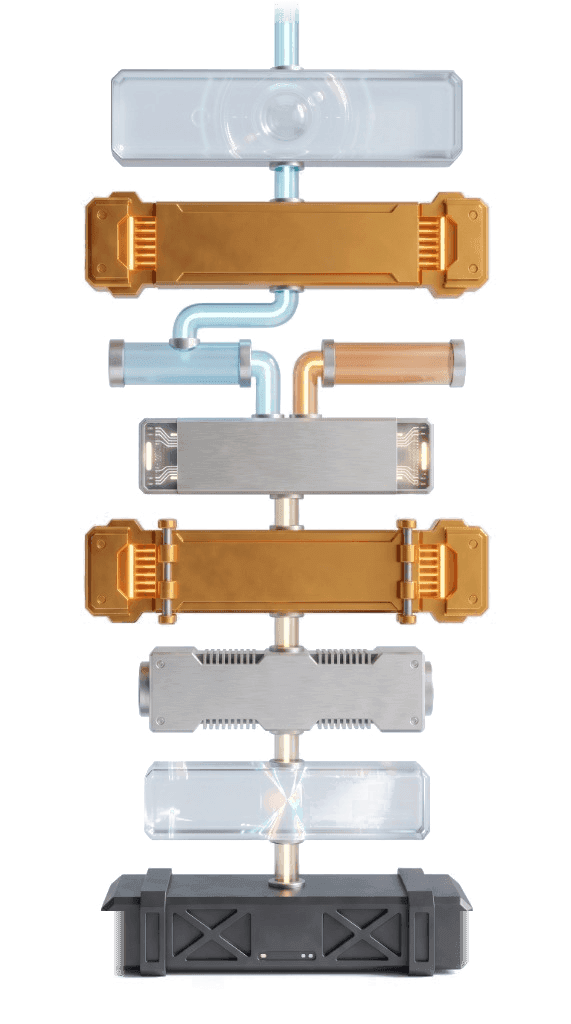
Channels feed one runtime; hard rules and AI live in separate layers; evidence underlies everything.

YAPRA Governed Platform Architecture 3D Schematic
Topology Modules (01–07)Tap to inspect
Selected Node01 // AGENT RUNTIME
Execution ModeDETERMINISTIC GATE
VerificationSHA-256 MERKLE RECEIPT
Latency SLA Target< 3.8ms HARD BOUND

Hard Boundary Containment

Probabilistic models never hold direct execution keys. Every intent is checked against deterministic rule engines and hard mathematical constraints before any state change occurs.

Cryptographic Receipts

Every prompt, response, policy verification, and tool dispatch produces an immutable SHA-256 Merkle receipt. Full retrospective auditability for SOC2, ISO 27001, and regulatory compliance.

Open MCP Standard

No proprietary walled gardens. Integrations use the standard Model Context Protocol (MCP) to connect bi-directionally to existing ERP, CRM, database, and internal tooling infrastructure.

01 Agent Runtime — (Understanding, Tool Routing, Execution)

High-order orchestrator that decomposes user intents, compiles execution plans into bounded DAGs, and dynamically dispatches sandboxed tool calls.

Kernel Guarantee: Zero unverified dispatch. Pre-flight DAG compilation halts immediately if an edge references an unregistered or unauthorized MCP endpoint.

Technical Deep-Dive: Decomposes unstructured requests into verifiable Directed Acyclic Graphs (DAG). Each task node is checked for strict permission schemas before being scheduled onto isolated worker threads.

  • Orchestration: Bounded DAG Dispatch
  • Verification: Pre-Flight Policy Gate
  • Isolation: Thread Sandboxing

02 Deterministic Core — (Rule-Based Logic & Hard Constraints)

Non-probabilistic policy engine enforcing organizational rules, legal boundaries, numerical thresholds, and compliance constraints before any action commits.

Kernel Guarantee: Fail-Closed Rule Evaluation. Invariant verification cannot be softened or bypassed by adversarial prompt engineering or model jailbreaking.

Technical Deep-Dive: Operates entirely outside of probabilistic neural weights. Enforces hard mathematical invariants, spend thresholds ($25k ceiling), and state machine rules at the CPU instruction level.

  • Constraint Type: Hard Mathematical Bound
  • Evaluation: O(1) Deterministic Check
  • Hallucination Risk: 0.000% (Non-LLM)

03 Model-Agnostic LLM — (Connect Any LLM: Claude, OpenAI, Gemini, Local)

Pluggable foundation models operating strictly in bounded advisory mode. Understanding fuzzy intent and drafting actions — AI output is strictly a proposal, never an executable command.

Kernel Guarantee: Advisory-only isolation. Model responses are treated as untrusted external inputs until parsed and passed through Gate 01 & Gate 02.

Technical Deep-Dive: Provides vendor-agnostic abstraction layer. Model outputs are strictly typed as advisory proposals (AST JSON-RPC), preventing direct shell execution or database write permissions.

  • Supported LLMs: Claude, OpenAI, Gemini, Local (Llama)
  • Lock-in Risk: Zero (Vendor-Agnostic Routing)
  • Execution Rule: Advisory Only (Zero Direct Writes)

04 Tool Adapters (MCP) — (API Connectors & System Integrations)

Standardized Model Context Protocol (MCP) server endpoints enabling bi-directional, audited communication with SAP, Salesforce, Oracle, SQL, and internal APIs.

Kernel Guarantee: Ephemeral Capability Tokens. Tool permissions are scoped down to the single active transaction turn and expire upon Merkle receipt generation.

Technical Deep-Dive: Implements open MCP JSON-RPC protocol. Connects directly to legacy ERP, SCADA, and CRM endpoints without modifying existing enterprise firewall topologies.

  • Protocol: Model Context Protocol (MCP)
  • Channel Type: Bi-directional JSON-RPC
  • Protection: Circuit Breaker & Rate Gate

05 Evidence & Governance Bedrock — (Immutable Audit Trail & Cryptographic Ledger)

The cryptographic foundation of YAPRA. Every prompt, model output, policy verification, tool invocation, and DB write is indelibly hashed into a tamper-evident Merkle ledger.

Kernel Guarantee: Cryptographic non-repudiation. Every turn receipt is cryptographically chained to the previous ledger state root, creating an indelible tamper-evident timeline.

Technical Deep-Dive: Maintains an immutable append-only Merkle ledger. Each state transition computes a cryptographic root binding the exact user prompt, policy evaluation, and adapter response.

  • Audit Proof: SHA-256 Merkle Receipts
  • Access Control: Granular Multi-Tier RBAC
  • Compliance: SOC2 Type II / ISO 27001 Ready

06 Operational Store — (Real-Time State & Transactions)

High-throughput operational database cluster storing live system state, active user sessions, execution graphs, and ephemeral operational memory with ACID guarantees.

Kernel Guarantee: Strict ACID Transactions. If an action fails downstream, changes roll back cleanly with active circuit breakers to ensure zero orphaned partial writes.

Technical Deep-Dive: High-throughput distributed state engine managing transactional memory and execution checkpoints. Supports instant rollback if downstream adapters encounter transient network faults.

  • Consistency: Strict ACID Compliance
  • Latency: < 1.8ms State Read
  • Encryption: AES-256 (At-Rest & In-Flight)

07 Document Corpus — (Knowledge Base & Archives)

Enterprise document store containing SOPs, regulatory documentation, operational history, and technical specifications, indexed via hybrid vector + BM25 search.

Kernel Guarantee: Row-Level Security & Document Hashing. Documents retrieved into context windows are stamped with their SHA-256 commit hash for audit provenance.

Technical Deep-Dive: Dense HNSW vector indices fused with lexical BM25 algorithms. Employs reciprocal rank fusion (RRF) to retrieve authoritative enterprise knowledge, eliminating ungrounded extrapolation.

  • Search Index: Hybrid Vector + BM25
  • Grounding: Strict Citation Anchoring
  • Permissioning: ACL Pass-Through
Request Execution Lifecycle // The Gauntlet

Every Single Request. Strictly Gated by Invariants.

Before an autonomous agent can retrieve a tool, mutate enterprise data, or execute an API transaction, it passes through an immutable physical pipeline where ambiguous intent halts and unauthorized actions are physically blocked.

Hover or tap any module to inspect flow without blocking next steps
YAPRA Deterministic 7-Stage Policy Pipeline
1. Understanding: Intent TypingEntity resolution & parameter bounding
[GATE 1] Clarification Gate

Confidence ≥ 99.5% · Zero Speculation

If not confident: halt, clarify & retry

Keyword Channel
Semantic Channel
2. Tool Retrieval & Rank Fusion
Keyword & semantic channels merge via RRF
[GATE 2] Policy & Scope Gate

Deterministic Pre-Action Gate (PAG)

Physical policy block before execution

3. Execute via Governed Adapters
Sandboxed execution in isolated MicroVMs
4. Answer with Sources & Provenance
Cites exact document hashes & ledger
Recorded End to End: Full State Ledger
Input & output permanently written at every stage
GATE 01CONFIDENCE BOUNDARY
≥ 99.5% Confidence

[GATE 1] Clarification Gate · Deterministic Halt

Is the runtime completely confident in what is being asked? If confidence falls below 99.5%, or if any operational parameter is missing or conflicting, the system refuses to speculate or extrapolate. It immediately halts execution and escalates for human clarification before proceeding.

HALT CONDITIONConfidence < 99.5% triggers an immediate execution halt. Never extrapolate. Never guess. Halt, clarify, and retry.
Zero speculative assumptions cross this physical boundary.
2/8
2 DETERMINISTIC ISOLATION GATES ENFORCED BEFORE ADAPTER MUTATION
Deterministic RRF•ACID Rollback•SHA-256 State Ledger

STAGE 01: Request Ingestion & Entity Resolution (STAGE 01 // COGNITIVE INGESTION)

When an operational payload, user prompt, or automated workflow trigger enters the runtime, YAPRA parses the syntax to determine the exact intent and resolve all referenced domain entities, system parameters, and target resources before formulating any execution plan.

Guarantee: Zero unmapped, ambiguous, or synthetic entity references ever enter the active runtime. (Parsing Latency: 0.24ms)

GATE 01: [GATE 1] Clarification Gate · Deterministic Halt (CRITICAL INVARIANT // CONFIDENCE BOUNDARY)

Is the runtime completely confident in what is being asked? If confidence falls below 99.5%, or if any operational parameter is missing or conflicting, the system refuses to speculate or extrapolate. It immediately halts execution and escalates for human clarification before proceeding.

HALT CONDITION: Confidence < 99.5% triggers an immediate execution halt. Never extrapolate. Never guess. Halt, clarify, and retry.

Guarantee: Zero speculative assumptions cross this physical boundary. (Halt Threshold: ≥ 99.5% Confidence)

STAGE 02: Dual-Channel Tool & Service Search (STAGE 02 // DUAL-CHANNEL RETRIEVAL)

To fulfill the verified request, YAPRA searches across candidate enterprise tools, internal microservices, and operational data connectors using parallel exact-match keyword matching and dense semantic vector embedding pipelines.

Guarantee: Dual indexing eliminates vector drift and prevents ungrounded tool invocations. (Dual Indexing: Lexical + Vector)

STAGE 03: Tool Shortlisting & Rank Fusion (STAGE 03 // RECIPROCAL RANK FUSION)

Candidate tools from both keyword and semantic channels are merged using Reciprocal Rank Fusion (RRF). Irrelevant utilities and peripheral APIs are pruned, producing a minimal, high-precision shortlist strictly matching the task requirements.

Guarantee: Guarantees minimal, high-precision tool surface exposure under complex payloads. (Pruning Ratio: Top 0.8% Shortlist)

GATE 02: [GATE 2] Pre-Action Gate (PAG) · Policy & Scope Physical Block (PRE-ACTION GATE (PAG) // SARC GOVERNANCE ARCHITECTURE)

Software structurally checks proposed actions against configured policies before tool invocation using the SARC (State, Action space, Reward, Constraints) governance architecture. Constraints are enforced as first-class runtime objects: if an action violates hard constraints, spending caps, or role hierarchies, it is immediately blocked before network dispatch. No action is executed.

POLICY & SARC CONSTRAINT BLOCK: Structurally validates policy scopes, spending caps, and authorization predicates. Violating any hard constraint triggers an immediate execution block. No action is executed.

Guarantee: Deterministic policy boundaries and SARC first-class constraints ensure zero unauthorized actions cross into production. (Framework: PAG & SARC Governance)

STAGE 04: Governed Adapter Execution (STAGE 04 // GOVERNED RUNTIME)

Authorized actions execute strictly through sandboxed, governed adapters into your core production systems, internal services, and message brokers—enforcing ACID transactional consistency, rate limits, and sub-millisecond rollback mechanisms.

Guarantee: Transactional isolation ensures zero operational blast radius across production backbones. (Isolation: Ephemeral MicroVM)

STAGE 05: Cryptographic Attribution & Source Verification (STAGE 05 // FACTUAL GROUNDING)

Every generated answer, summary, or confirmation explicitly cites its exact source document hash, record timestamp, and schema version from authoritative systems of record. Unsourced or unsubstantiated claims are discarded.

Guarantee: 100% provenance verification anchored directly to cryptographic document signatures. (Attribution: SHA-256 Provenance)

STAGE 06: Immutable End-to-End Audit Ledger (STAGE 06 // IMMUTABLE AUDIT TRAIL)

By construction, every stage of execution—initial request payload, intent typing, gate verifications, intermediate thoughts, tool calls, and final response—is permanently recorded into an append-only cryptographic state journal for continuous regulatory compliance.

Guarantee: Permanent, tamper-proof auditability satisfying SOC2, HIPAA, and ISO 27001 standards. (Compliance: SOC2 / HIPAA / ISO)

Governed Agents · Deterministic Runtime

Hands off. Still in control.

Autonomous agents that plan, adapt, and execute solely within your enterprise data perimeter. Complete hands-off execution, backed by mathematically proven deterministic control.

Private Data Perimeter

Zero weights training leakage. Learns and adapts exclusively to your proprietary enterprise data.

Governed Execution with Hard Invariants

Every proposed tool call and parameter payload is verified by deterministic pre-flight policy gates before any API is mutated.

Cryptographic SHA-256 Receipts

Every executed turn produces an immutable cryptographic proof on the sovereign state ledger.

yapra-gauntlet.turn
100% INVARIANT HOLD
Step 01 // Intent Ingestion

Agent Action Proposal

db.mutate_orders()

Tool Call Payload
↓ Deterministic Policy Gates
Gate 01 // Boundary VerificationPASSED 0.2ms
Spend & Privilege Ceiling
Gate 02 // Sandbox InvariantsVERIFIED 0.4ms
Dry-Run State Verification
↓ Merkle State Commit
Step 03 // Immutable Proof

Cryptographic State Receipt

SHA-256 SIGNED & SEALED

Atomic State Commit
Simulate Invariant:
Live Turn Log Feed (Automated Sandbox)
Real-time Invariant Interceptions
10:48:21agent.rebalance_portfolio()PRE-FLIGHT GATE: PASSED
0.3ms
10:48:23agent.synthesize_schema()SANDBOX VERIFIED: PASSED
0.5ms
10:48:25agent.elevate_admin_role()INTERCEPTED [Invariant Breach]
0.1ms
10:48:28agent.commit_state_receipt()IMMUTABLE AUDIT SIGNED
1.2ms

Scenario 1: Nominal Path (Pass)

All deterministic gates pass: Intent parsed with 99.8% confidence (>= 99.5% threshold), Gate 01 Clarification Gate passed, authorized tool shortlisted, Gate 02 Policy & Scope Gate verified ($24,500 within $25,000 ceiling), PO committed via ERP Adapter with ACID guarantee, and SHA-256 receipt sealed in Merkle ledger.

Scenario 2: Ambiguous Intent (Gate 01 Pause — Never Guess)

Ambiguous operator request detected (Confidence 58% < 99.5% threshold). Gate 01 Clarification Gate deterministically halts execution and prompts the human operator to clarify parameters before any tool invocation. Stopping to ask is a verified success path, not an error.

Scenario 3: Scope Breach (Gate 02 Block — Hard Boundary Rejection)

High-risk request ($150,000 emergency contractor invoice) exceeds role spending ceiling ($25,000). Gate 02 Pre-Action Policy Gate deterministically blocks execution before network dispatch with zero blast radius.

Scenario 4: Predictive Maintenance Lifecycle (SCADA → ERP → Work Order)

End-to-end closed-loop workflow: [01] SCADA Telemetry detects Turbine #04 bearing vibration spike (4.8 mm/s > 4.2 threshold) → [02] Live Operational Entity Graph traverses dependencies to Assembly Line 2 and identifies Ceramic Bearing SKF-6208 → [03] ERP Adapter verifies 3 units in Warehouse A Bay 12 and assigns Shift 2 window → [04] Work Order #44019 synthesized with torque specs & LOTO safety checklist → [05] Plant Lead human signoff confirmed under L3 Autonomy → [06] Work Order dispatched to ERP queue and sealed with SHA-256 Merkle receipt.

Graduated Trust Architecture

Autonomy Levels Matrix

Enterprise autonomy is not all-or-nothing. Adopt governed agents gradually, starting with advisory shadows and escalating to autonomous fleets under hard boundary rules.

LEVEL 01

Advisory & Shadow Analysis

HUMAN DECIDES

Agents observe telemetry, inspect document corpora, and draft recommendations. No write access to internal systems or APIs is granted. Humans execute all actions manually.

Proposal Only
LEVEL 02

Gated Human-in-the-Loop

HUMAN APPROVES

Agents formulate complete transaction payloads (e.g. ERP purchase orders, maintenance schedules). Deterministic gates pause execution until designated operators sign off with one-click approval.

Prepared Commit
LEVEL 03

Bounded Autonomous Execution

GOVERNED AUTONOMY

Agents act autonomously as long as parameters stay within mathematically enforced limits (e.g. transactions < $25,000, known vendor list, invariant safety margins). Exceeding bounds halts execution.

Autonomous within Invariants
LEVEL 04

Systemic Multi-Agent Fleet

FLEET ORCHESTRATION

Specialized autonomous agents communicate across departments via Model Context Protocol (MCP). Every agent handoff is signed with cryptographic proofs, preventing cascade failures.

Decentralized Swarm Governance
LEVEL 03 Deep Dive

Bounded Autonomous Execution

Containment: Strict Mathematical Boundaries
Human Oversight Model

Automated Circuit Breaker

Cryptographic Audit Trail

Full Turn SHA-256 Merkle Receipt

Bounded Blast-Radius Isolation

Enforced by Deterministic Gates

LEVEL 01: Advisory & Shadow Analysis (HUMAN DECIDES)

Agents observe telemetry, inspect document corpora, and draft recommendations. No write access to internal systems or APIs is granted. Humans execute all actions manually.

Role: Proposal Only | Containment: Read-Only Environment | Human Control: 100% Manual Execution | Audit Trail: Advisory logs hashed to Merkle tree

LEVEL 02: Gated Human-in-the-Loop (HUMAN APPROVES)

Agents formulate complete transaction payloads (e.g. ERP purchase orders, maintenance schedules). Deterministic gates pause execution until designated operators sign off with one-click approval.

Role: Prepared Commit | Containment: Stage 2 & 4 Hard Pause | Human Control: Pre-flight Operator Gate | Audit Trail: Operator identity & receipt sealed

LEVEL 03: Bounded Autonomous Execution (GOVERNED AUTONOMY)

Agents act autonomously as long as parameters stay within mathematically enforced limits (e.g. transactions < $25,000, known vendor list, invariant safety margins). Exceeding bounds halts execution.

Role: Autonomous within Invariants | Containment: Strict Mathematical Boundaries | Human Control: Automated Circuit Breaker | Audit Trail: Full Turn SHA-256 Merkle Receipt

LEVEL 04: Systemic Multi-Agent Fleet (FLEET ORCHESTRATION)

Specialized autonomous agents communicate across departments via Model Context Protocol (MCP). Every agent handoff is signed with cryptographic proofs, preventing cascade failures.

Role: Decentralized Swarm Governance | Containment: Cross-Tenant Merkle Verification | Human Control: Fleet Kill-Switch & Dynamic Quorum | Audit Trail: Distributed Indelible Ledger

Cryptographic Proof Infrastructure

Security, Governance & Receipts

In enterprise operations, AI cannot be a black box. YAPRA seals every prompt, policy evaluation, tool invocation, and state mutation into an indelible, verifiable audit trail.

Deterministic Structural Invariants

The 6 Sovereign Boundaries

Mathematical constraints baked directly into the kernel. These gates cannot be bypassed by high model confidence or prompt manipulation.

Isolation by Default
01 // DATA LAYER ISOLATION

Isolation by Default

Tap to inspect schema
01
01 // DATA LAYER ISOLATION

Isolation by Default

One installation per organization. Your own database, storage, and indexes. Row-level access governed in the data layer, not application goodwill.

SOC2 CC6.1, CC6.3
Inspect Proof
Un-bypassable Gates
02 // DETERMINISTIC AUTH

Un-bypassable Gates

Tap to inspect schema
02
02 // DETERMINISTIC AUTH

Un-bypassable Gates

Every action passes deterministic authorization and scope checks after the model proposes, before execution runs.

SOC2 CC6.8
Inspect Proof
Proposal, Not Command
03 // PROMPT INJECTION DEFENSE

Proposal, Not Command

Tap to inspect schema
03
03 // PROMPT INJECTION DEFENSE

Proposal, Not Command

The core defense against prompt injection. The blast radius of a bad suggestion is strictly bounded by architecture.

OWASP Top 10 for LLM (LLM01, LLM02)
Inspect Proof
Least-Privilege Tool Access
04 // SCOPED ADAPTER CAPABILITIES

Least-Privilege Tool Access

Tap to inspect schema
04
04 // SCOPED ADAPTER CAPABILITIES

Least-Privilege Tool Access

Agents see only tools their scope grants. Unauthorized requests are rejected. The platform fails closed, not open.

SOC2 CC6.2, CC6.3
Inspect Proof
Secrets Out of Reach
05 // CREDENTIAL ENCLAVE

Secrets Out of Reach

Tap to inspect schema
05
05 // CREDENTIAL ENCLAVE

Secrets Out of Reach

Credentials live in environment configuration only. Traces record everything except raw secrets, which are scrubbed by design.

SOC2 CC6.6
Inspect Proof
Absolute Attribution
06 // MERKLE AUDIT TRAIL

Absolute Attribution

Tap to inspect schema
06
06 // MERKLE AUDIT TRAIL

Absolute Attribution

Every action answers: what happened, on whose authority, and under which approved version. Detection and audit come built in.

EU AI Act Art. 12 (Record-keeping)
Inspect Proof

Invariant 01 (DATA LAYER ISOLATION): Isolation by Default

One installation per organization. Your own database, storage, and indexes. Row-level access governed in the data layer, not application goodwill.

Mathematical Guarantee: Dedicated tenant VPC, dedicated Postgres schema, strict Row-Level Security (RLS) enforced at the database engine level.

Threat Vector Mitigated: Cross-tenant data contamination, multi-tenant memory bleed, prompt leakage across enterprise boundaries.

Compliance Standard: SOC2 CC6.1, CC6.3 · ISO 27001 A.9.4.2 · GDPR Art. 32

Invariant 02 (DETERMINISTIC AUTH): Un-bypassable Gates

Every action passes deterministic authorization and scope checks after the model proposes, before execution runs.

Mathematical Guarantee: Code decides, not LLM confidence. Pre-execution interceptors validate schema, ceiling limits, and AST structure before any tool dispatch.

Threat Vector Mitigated: Hallucinatory execution, unauthorized API mutations, rogue recursive agent loops.

Compliance Standard: SOC2 CC6.8 · NIST SP 800-53 AC-3 · ISO 27001 A.9.4.5

Invariant 03 (PROMPT INJECTION DEFENSE): Proposal, Not Command

The core defense against prompt injection. The blast radius of a bad suggestion is strictly bounded by architecture.

Mathematical Guarantee: LLMs are treated as untrusted advisory entities. They output structured proposals (JSON-RPC), never direct shell or DB commands.

Threat Vector Mitigated: Direct prompt injection, jailbreaking, indirect RAG injection payloads.

Compliance Standard: OWASP Top 10 for LLM (LLM01, LLM02) · MITRE ATLAS AML.T0054

Invariant 04 (SCOPED ADAPTER CAPABILITIES): Least-Privilege Tool Access

Agents see only tools their scope grants. Unauthorized requests are rejected. The platform fails closed, not open.

Mathematical Guarantee: Ephemeral Model Context Protocol (MCP) server scopes. Tools are selectively bound to individual task turns, expiring on commit.

Threat Vector Mitigated: Privilege escalation, lateral movement across corporate toolchains, excessive agent permissions.

Compliance Standard: SOC2 CC6.2, CC6.3 · NIST SP 800-53 AC-6 · Zero Trust Architecture

Invariant 05 (CREDENTIAL ENCLAVE): Secrets Out of Reach

Credentials live in environment configuration only. Traces record everything except raw secrets, which are scrubbed by design.

Mathematical Guarantee: Credentials reside inside dedicated KMS hardware security modules. The agent runtime receives opaque proxy handles, never plaintext keys.

Threat Vector Mitigated: Credential exfiltration via prompt leak, accidental secret dumping in LLM context windows.

Compliance Standard: SOC2 CC6.6 · PCI-DSS Req 3.4 · ISO 27001 A.10.1

Invariant 06 (MERKLE AUDIT TRAIL): Absolute Attribution

Every action answers: what happened, on whose authority, and under which approved version. Detection and audit come built in.

Mathematical Guarantee: Every turn computes a SHA-256 Merkle root binding the user prompt, document hashes, model weights version, gate checks, and adapter output.

Threat Vector Mitigated: Non-repudiation failures, unverified AI decision chains, regulatory audit failure.

Compliance Standard: EU AI Act Art. 12 (Record-keeping) · SOC2 CC7.2 · HIPAA § 164.312(b)

SHA-256 Merkle Receipts

Every turn computes a cryptographic digest linking the exact user prompt, loaded document versions, gated policy evaluations, model proposal, and adapter execution.

Indelible Third-Party Verification

ACID State & Transactional Rollback

Dispatched actions to ERP, CRM, or SCADA are wrapped in atomic transactions with active circuit breakers. If an invariant fails downstream, changes roll back cleanly.

Zero Orphaned Partial Writes

SOC2 Type II & ISO 27001 Ready

Architected for compliance out of the box. Strict single-tenant isolation, row-level AES-256 encryption at-rest, TLS 1.3 in-transit, and role-based access control (RBAC).

Engineered for EU AI Act & DORA Compliance
RECEIPT SAMPLE // SHA-256 MERKLE LEAF
STATUS: MATHEMATICALLY SEALED

// Transaction Turn Receipt ID: tx_984a_20260917_0042

merkle_root: "7f83b1657ff1fc53b92dc18148a1d65dfc2d4b1fa3d677284addd200126d9069"

turn_hash: "3b9fa81c628e932b145d82a1789c02ff438b01a2f1c849e7b4e9182371a5cd19"

deterministic_gates: [

{ "gate": "GATE_01_CLARIFICATION", "status": "PASS", "confidence": 0.998 },

{ "gate": "GATE_02_POLICY_SCOPE", "status": "PASS", "ceiling_usd": 25000, "amount_usd": 24500 }

]

adapter_dispatch: { "protocol": "MCP_ERP_INVENTORY", "idempotency_key": "idem_88219_commit" }

// Invariant: Code decides. Deterministic boundary enforcement guaranteed.

DEPLOYMENT SOVEREIGNTY

Provable exit and absolute deployment sovereignty.

Your installation runs alone, on its own data, behind your own controls. Answered by architecture, not hopeful contract language.

Air-Gapped / Enclaves: 100% Local models, 0.00% egress.
Commercial APIs (Hybrid): Client-side PII scrubbing & pre-flight policy interception.
01Fastest Enterprise Deployment

Single-Tenant Private Cloud (VPC)

Dedicated cloud installations featuring single-tenant databases, isolated vector indexes, and customer-held KMS keys.

Tap to collapse specifications ↑
SOVEREIGN TOPOLOGY
VPC TENANCY: 100% SINGLE-TENANT
Single-Tenant Private Cloud (VPC)

Engineered for organizations requiring strict boundary isolation within their existing cloud perimeter. Your environment operates in dedicated single-tenant VPC containers with private databases, dedicated vector indexes, and zero co-mingled prompts.

Database Isolation
Dedicated PostgreSQL
Vector Index
Customer-Isolated Qdrant
Context Co-mingling
0.00% (Strictly Isolated)

Zero shared memory, storage, or execution threads across enterprise tenants.

02Air-Gapped Sovereignty

Air-Gapped On-Premises

Full physical control within your data center or bare-metal clusters, completely disconnected from WAN with zero telemetry egress.

Tap to view details & 3D model ↓
03Maximum Fortification

Sovereign Hardware Enclaves

Hardware-enforced memory encryption and cryptographic attestation (AWS Nitro Enclaves, AMD SEV-SNP, Intel SGX).

Tap to view details & 3D model ↓

No Vendor Lock-In. Learned states, models, and data export byte-for-byte with mathematically verified restore capabilities.

01. Single-Tenant Private Cloud (VPC) — Dedicated Customer Cloud · AWS, Azure, GCP & EU Sovereignty (MANAGED SOVEREIGNTY)

Dedicated cloud installations featuring single-tenant databases, isolated vector indexes, and customer-held KMS keys.

Engineered for organizations requiring strict boundary isolation within their existing cloud perimeter. Your environment operates in dedicated single-tenant VPC containers with private databases, dedicated vector indexes, and zero co-mingled prompts.

Architectural Rule: Zero shared memory, storage, or execution threads across enterprise tenants.

  • Tenancy Isolation: 100% Single-Tenant (Zero shared memory, database, or indexes)
  • Network Boundary: Hardened VPC, TLS 1.3 Strict, Dedicated Ingress Gateway
  • Storage & Residency: Dedicated PostgreSQL + Qdrant Vector Index (Customer Isolated)
  • Inference Serving: High-Throughput Dedicated Inference Bandwidth
  • Audit Ledger: Immutable SHA-256 Cryptographic Audit Ledger
  • Compliance: SOC2 Type II Ready, ISO 27001 Prepared, GDPR & KVKK Aligned
  • Operated & continuously monitored inside your dedicated cloud account
  • Dedicated database, vector storage, and episodic memory index
  • Zero co-mingling of enterprise prompts or context windows
  • Structured rollout: Week 1 scoping, Weeks 2–3 isolated pilot deployment

02. Air-Gapped On-Premises — Customer Data Center & Bare-Metal Hardware Sovereignty (TOTAL PHYSICAL DOMAIN)

Full physical control within your data center or bare-metal clusters, completely disconnected from WAN with zero telemetry egress.

Built for defense, banking, healthcare, and critical infrastructure where enterprise data can never cross corporate or sovereign perimeters. Operates inside customer data centers on bare-metal servers or local Kubernetes clusters with zero external WAN connectivity.

Architectural Rule: Hardware-level physical sovereignty. Enterprise data, models, and receipts remain strictly within customer custody.

  • Tenancy Isolation: Total On-Premises Hardware Ownership (Bare-Metal / Air-Gap)
  • Network Boundary: Isolated Local Physical Bus, Zero External WAN Ingress/Egress
  • Storage & Residency: Customer-Owned Enterprise SAN / Self-Encrypting Drives (SED)
  • Inference Serving: On-Premise GPU Cluster / Enterprise AI Accelerator Support
  • Audit Ledger: Internal Hardware Security Module (HSM) Key Signing
  • Compliance: Defense Grade, Banking Tier-1 Compliant, Sovereign Mandates
  • Zero external network telemetry, zero diagnostic call-homes
  • Data never leaves your physical corporate security perimeter
  • Direct integration with internal LDAP / Okta SSO & HashiCorp Vault
  • Offline cryptographically signed receipts for every operational turn

03. Sovereign Hardware Enclaves — Confidential Computing & Cryptographic Memory Isolation (CONFIDENTIAL COMPUTING)

Hardware-enforced memory encryption and cryptographic attestation (AWS Nitro Enclaves, AMD SEV-SNP, Intel SGX).

The highest standard of cryptographic isolation in cloud and hybrid environments. Agent execution, model weights, and sensitive credentials run inside hardware-isolated enclaves where even cloud hypervisors, hosting providers, or root administrators cannot inspect or alter memory state.

Architectural Rule: Confidential computing guarantees that even root infrastructure operators cannot inspect runtime state or model memory.

  • Tenancy Isolation: Hardware-Enforced Cryptographic Attestation (Nitro / SEV-SNP)
  • Network Boundary: Cryptographically Attested Secure Local Vsock Channel
  • Storage & Residency: Ephemeral Memory-Only Decryption, Hardware HSM Key Management
  • Inference Serving: Enclave-Isolated Neural Inference & Deterministic Gate Execution
  • Audit Ledger: Hardware-Signed Cryptographic Receipts with Remote Attestation Proofs
  • Compliance: Confidential Computing Consortium, DORA, Zero-Trust Banking Standard
  • Cryptographically attested hardware isolation protects against hypervisor inspection
  • Zero plaintext exposure of proprietary models, prompts, or enterprise database records
  • Remote attestation verifies exact software hash before executing a single turn
  • Hardware-enforced zero network egress with cryptographic memory isolation
ENGAGEMENT & COMMERCIAL PROTOCOL

Service-as-a-Software: A rollout strategy gated by hard evidence.

You are not licensing static software — you are subscribing to work that gets done, monitored, and continuously adapted. Expansion happens only upon hard mathematical evidence.

01Onboarding Phase

Foundation Setup

One-Time Architectural Adaptation

Adapting your enterprise vocabulary, schemas, policy gates, and custom MCP adapters cleanly without code forks.

02Working Agent Service

Core Runtime Engine

Dedicated Per-Instance Subscription

Dedicated compute, continuous health telemetry, automated deterministic updates, and immutable SHA-256 receipts.

03Zero Budget Surprises

Predictable Scale

Metered Above Base Allowance

Generous base reasoning allowance with transparent turn-metering and impenetrable hard budget ceilings.

Service-as-a-Software Ascending Milestone Staircase
01 · TargetWeek 1 · Scoping
SCOPING & VALUE BOUNDARY

Pick one measurable problem

A scheduling, maintenance, or resource-planning pain felt weekly, countable in hours or capital.

Hard Evidence Gate

Identified countable loss in hours or capital signed off by enterprise domain stakeholders.

Verified Deliverables
✓Identification of one recurring workflow bottleneck
✓Extraction of domain vocabulary and rule boundaries
✓Clear definition of measurable success metrics

Zero-Risk Engagement Protocol. Every milestone is audited in your environment before wider scale. Expansion happens only upon hard mathematical evidence.

Stage 01: Target (Week 1 · Scoping) — Pick one measurable problem

A scheduling, maintenance, or resource-planning pain felt weekly, countable in hours or capital.

Scoping begins with zero code and zero risk. We identify a single, high-friction operational workflow where loss is countable in hours or capital, and define mathematical success thresholds with your domain owners.

Hard Evidence Gate: Identified countable loss in hours or capital signed off by enterprise domain stakeholders.

  • Identification of one recurring workflow bottleneck
  • Extraction of domain vocabulary and rule boundaries
  • Clear definition of measurable success metrics
  • Zero-risk feasibility sign-off before any instance launch

Stage 02: Isolate (Weeks 2–3 · Deployment) — Deploy the isolated instance

Your dedicated installation, your data, your access rules. Nothing shared, nothing irreversible.

Your agent runs in digital isolation inside your secured perimeter. We connect read-only enterprise tools through governed Model Context Protocol (MCP) adapters. No shared surfaces, nothing irreversible.

Hard Evidence Gate: Zero shared surfaces, verified single-tenant isolation, immutable boundary rules verified by security.

  • Turnkey provisioning of isolated customer instance (VPC or On-Prem)
  • Deterministic policy gate configuration for tools and database access
  • Integration of read-only enterprise MCP adapters
  • Strict circuit-breaker safeguards preventing irreversible state mutation

Stage 03: Measure (Weeks 4–6 · Verification) — Measure in your numbers

The first result is designed to arrive in weeks and be counted by you, not presented by us.

Inspect verifiable results in your live environment. Outcomes are measured and audited by your internal team using your real corporate telemetry, not delivered as biased vendor sales charts.

Hard Evidence Gate: Internal verification by customer stakeholders using real corporate telemetry and SHA-256 receipts.

  • Auditing of live transactions against SHA-256 cryptographic receipts
  • Comparative benchmarking against manual operational baselines
  • Hard accounting of saved labor hours and eliminated discrepancies
  • Formal executive review presentation with audited customer data

Stage 04: Expand (Month 2+ · Governed Scale) — Widen only on evidence

Each next domain is earned by the measured success of the previous one. Zero blanket commitments.

Rollout advances one verified milestone at a time. If the system does not prove unmistakable value in your data, it does not earn the next expansion phase. Expansion is governed, predictable, and evidenced-backed.

Hard Evidence Gate: System earns its expansion; zero blanket commitments without mathematically proven value.

  • Sequential rollout to adjacent business units and operational pipelines
  • Transition from Level 2/3 supervisory autonomy to Level 4 execution
  • Autonomous fleet updates without breaking custom policy configurations
  • Continuous immutable audit ledger maintenance across all corporate units
YAPRA Logo
yapra.ai

Deterministic Control for Autonomous Systems. Governed Agents with Hard Boundary Rules and Cryptographic Receipts.

SOC2 Type II Ready // ISO 27001 Prepared
2U1K International
Powered by2U1K International GmbH

Integrations

  • Enterprise Systems
  • Enterprise ERP (MM / SCM)
  • Enterprise CRM & Service
  • OPC-UA / MQTT (SCADA)
  • Model Context Protocol (MCP)

Enterprise

Initiate an evidence-gated scoped pilot directly inside your dedicated VPC or on-premises perimeter.

© 2026 yapra.ai. All rights reserved. Deterministic Governed Core.

Frequently Asked Questions — YAPRA Architectural & Technical Specifications

What is YAPRA and how does it differ from developer prompt frameworks?
YAPRA is not a probabilistic prompt library or a conversational chatbot. Traditional frameworks provide developer scaffolding, but leave boundary enforcement to the LLM itself ("hoping the model respects system instructions"). YAPRA is a sovereign, deterministic platform core that sits between neural reasoning and enterprise production systems. It enforces immutable policy gates, hard spend ceilings, and cryptographic state receipts compiled in deterministic code—guaranteeing zero unsigned mutation and deterministic execution boundary enforcement.
How do Deterministic Policy Gates prevent database corruption or unauthorized mutations?
YAPRA enforces a 7-stage request pipeline with a Pre-Action Gate (PAG) grounded in the SARC (State, Action space, Reward, Constraints) governance architecture. Every proposed tool invocation, API call, or ERP mutation is intercepted before a single network packet is dispatched. If a proposed mutation exceeds role-based authorization, breaches budgetary ceilings, or violates predefined invariants, the gate blocks execution locally. Unauthorized API mutations are structurally and cryptographically blocked before dispatch.
What deployment models are supported, and can YAPRA run completely air-gapped?
Yes. YAPRA supports three primary deployment architectures: (1) Single-Tenant VPC hosted in dedicated customer clouds (AWS, Azure, GCP, or EU sovereign clouds); (2) Air-Gapped On-Premises operating inside customer-owned data centers completely disconnected from the public Internet with zero telemetry egress; and (3) Sovereign Hardware Enclaves utilizing hardware-isolated confidential computing (e.g., AWS Nitro Enclaves, AMD SEV-SNP).
What are Cryptographic Merkle Receipts and what do they actually prove?
Every action, evaluation, and state mutation within YAPRA is hashed sequentially into a tamper-evident Merkle tree and sealed with a SHA-256 root receipt. Combined with customer-managed KMS/HSM key signing and monotonic sequence ordering, this guarantees mathematical non-repudiation: external auditors (internal audit, Big 4, regulatory bodies) can cryptographically verify that a specific policy evaluation and authorization snapshot was committed in an immutable sequence and has not been altered, forged, or backdated after the fact. It establishes verifiable record integrity for audit trails under EU AI Act and DORA mandates.
How does YAPRA model an organization (equipment, ERP inventory, and personnel)?
YAPRA maintains an active Operational Entity Graph that unifies equipment telemetry, live ERP inventory, technician shift schedules, and financial delegation matrices. When an event occurs (e.g., sensor drift on a turbine or an ERP supply stockout), the engine re-evaluates all dependent maintenance jobs and schedules. Recommendations are grounded in real operational constraints, and human operators retain final signoff. All organizational graph data is stored in open standards (PostgreSQL, vector index, MCP schemas) with full Provable Exit rights.
How does YAPRA assist with the EU AI Act, DORA, and SOC2 / ISO 27001 requirements?
Under the EU AI Act, high-risk autonomous agents require continuous risk management (Article 9), immutable logging (Article 12), and human-in-the-loop oversight (Article 14)—all natively enforced by YAPRA’s 4 Autonomy Levels and Merkle logs. For financial institutions under DORA, YAPRA guarantees operational resilience through deterministic rollback simulations and instant break-glass kill switches. The platform is engineered to a SOC2 Type II Ready // ISO 27001 Prepared operational standard.
What does "Provable Exit" mean and how does YAPRA eliminate vendor lock-in?
Provable Exit guarantees that the enterprise maintains complete sovereignty over its operational IP. Because YAPRA is built on open standards—such as the Model Context Protocol (MCP), standard SQL/PostgreSQL databases, and open REST/GraphQL interfaces—you can export all policy rulebooks, telemetry history, Merkle receipt ledgers, and agent workflows at any time with zero proprietary platform lock-in.
What is the SARC Framework and how does it enforce runtime governance?
SARC (State, Action space, Reward, Constraints) is an architectural governance framework for agentic systems that treats constraints as first-class specification objects alongside state, action space, and reward. Rather than relying on soft prompts, dashboards, or post-hoc auditing, SARC compiles operational constraints directly into runtime enforcement sites—primarily the Pre-Action Gate (PAG) and Post-Action Auditor (PAA). It validates authorization predicates, spending limits, and execution safety before tool dispatch, deterministically blocking unauthorized mutations with zero blast radius.
How does an enterprise begin deploying YAPRA?
YAPRA utilizes an evidence-gated 4-stage rollout (Service-as-a-Software): (01) Target (Week 1 · Scoping — identify one measurable operational bottleneck countable in hours or capital); (02) Isolate (Weeks 2–3 · Deployment — deploy a dedicated single-tenant instance in your VPC or on-premises with read-only MCP adapters and zero shared surfaces); (03) Measure (Weeks 4–6 · Verification — audit live operational ROI in your own numbers backed by SHA-256 receipts); and (04) Expand (Month 2+ · Governed Scale — widen to adjacent workflows only upon hard mathematical evidence). Enterprises can initiate Stage 01 by clicking Start a Scoped Pilot.
Enterprise Design Partner Program — Work Directly with YAPRA Architects on Your First Governed Workflow

We partner with select enterprises to deploy bounded autonomous agents inside their own VPC or on-premises environment. Experience measurable ROI on a scoped business process before broad rollout. 2026 Enterprise Cohort: Limited to 5 Enterprises.